
Compliance consulting
Start with a clear answer: does the regulation apply to you at all? And if so, what do you actually need to do?
Built for ISO 27001NIS2 DORA
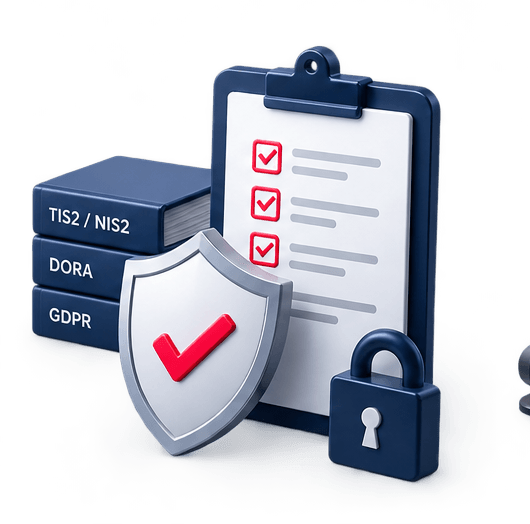
- Applicability assessment
- Gap analysis
- Action plan
The first step is understanding what really applies to you
NIS2, DORA, GDPR: there are many requirements and little clarity. The first step is always the same: find out what specifically applies to your company and how much of it you already meet.
During the consultation we review your situation and give you a realistic plan, with no unnecessary work and no scare tactics. It often turns out that part of the requirements is already implemented, just not documented anywhere.
How we can help
From the first question, "does this apply to us?", to audit preparation.
Applicability assessment
Gap analysis
Action plan
Implementation support
Audit preparation
Supplier and contract review
Incident reporting procedure
Management training
Frequently asked questions (FAQ)
How do we find out whether NIS2 applies to our company?
It depends on your sector, the size of the company and whether you are part of the supply chain of an essential service. Quite a few companies are affected indirectly, as suppliers to a regulated customer. That is exactly what we clarify in the first consultation.
How do NIS2 and DORA differ?
NIS2 covers a wide range of sectors and sets general cybersecurity management requirements. DORA is aimed at the financial sector and is more detailed, especially on business continuity, testing and oversight of ICT third-party providers. Some companies have to comply with both.
Does a consultation mean we will have to buy a lot of services?
No. The goal of the consultation is clarity. Often the conclusion is that a few targeted changes and documentation are needed, not new infrastructure. What to do next, and with whom, is your decision.
How long does it take to prepare for the requirements?
It depends on the starting point. For a company that already has well-managed IT support and protection, a few months to sort out documentation and processes is often enough. If you start from zero, a realistic timeline is six months to a year.
Related services
DORA implementation from A to Z
We will help you implement DORA, from policies to deploying security solutions.
NIS2 implementation from A to Z
We will help you implement NIS2, from policies to deploying security solutions.
Expertise confirmed by certifications
This service is delivered by specialists with valid international certifications. Their expertise is confirmed by independent organisations, not by us.
-
ISO/IEC 27001 Lead Implementer
The service is delivered in line with the requirements of an ISO/IEC 27001 management system.
-
Certified Information Security Manager
Security governance, policies and incident processes following the ISACA methodology.
-
Certified Information Systems Auditor
Audit and evidence in line with international information systems audit standards.
Order a compliance consultation
We reply within 1 business day